Seven ISMS platforms scored on Statement of Applicability automation, Annex A control mapping and ISO 27001 audit path. Sprinto leads at 84 out of 100, Nov 2026.
Score 5 of 5 on automated evidence, worth 20 of 100 points
Full marks on frameworks
6 of 7
The five core frameworks plus three or more of ISO 42001, NIST, FedRAMP or CMMC
Audit sold with the platform
1 of 7
The audit comes in the platform deal or from an affiliated audit firm
The best ISMS software among the seven scored here is Sprinto, at 84 out of 100. Vanta follows at 82, then Drata at 76, Secureframe at 75, Scrut at 72, OneTrust at 64 and Thoropass at 52. All seven cover ISO 27001, and all are scored on the same rubric.
Sprinto says it drafts the Statement of Applicability on day one and automates evidence for Annex A controls. Vanta says it generates the SoA automatically and supports ISO 27017, 27018 and 27701 extensions. Thoropass scores lowest overall but runs the ISO 27001 audit through Thoropass Certification LLC, its accredited ISO 27001 certification subsidiary. Buyers evaluating DACH-specific options also meet DataGuard, Secfix and HiScout, which sit outside the scored set.
Best for ISO 27001 certification delivered by Thoropass Certification LLC, its accredited ISO 27001 subsidiary
52/100
No list price.
Delivered in-platform by Thoropass Assurance, a licensed CPA firm
4.7/5 (585 G2)
What ISMS software covers
ISO/IEC 27001:2022 requires an organization to establish, implement, maintain and continually improve an information security management system. The standard requires a scope statement, a risk assessment, a Statement of Applicability and the Annex A controls the organization has selected and justified.
ISMS software handles the documentation layer: drafting and updating the SoA, mapping Annex A controls to evidence, tracking policy approvals and linking supplier assessments to the controls in Annex A 5.19 to 5.23. It also gives a certification body or external auditor a controlled view of evidence when the certification audit runs. The ISO 27001 cost guide breaks that audit out as a line of its own.
Compliance management software covers many of the same components for other frameworks alongside ISO 27001, and GRC software adds enterprise risk and governance on top of that.
How we ranked these
All seven platforms rank on the same eight-criterion rubric as every other ranking on this site. The criteria run in priority order by weight: automated evidence (20 points), framework coverage and audit path (15 each), then pricing transparency, trust and questionnaires, vendor risk management, customisation and user sentiment (10 each).
For an ISMS buyer, three criteria carry extra weight. Audit path measures how close the platform gets a team to a signed certificate. Customisation asks whether a team can build Annex A controls or tests the vendor did not ship. Vendor risk measures supplier assessment tools. A capability counts when the vendor lists it on any plan or add-on.
1. Sprinto: Best overall for ISMS scope, SoA and Annex A evidence automation
84/100
Strong (70 to 84)
Sprinto features
Sprinto ranks first at 84 out of 100 on the ISMS angle. Sprinto says it scopes the ISMS against the technology stack on day one and drafts the risk register, policies and Statement of Applicability for the team to approve. Its integrations feed continuous evidence for Annex A controls, and Sprinto says the same Annex A mapping reuses across its 200+ digitized frameworks so a team running ISO 27001 alongside SOC 2 or GDPR does not rebuild controls. Sprinto also covers Annex A 5.19 to 5.23, the supplier security controls, through its vendor risk module, which earns 5 of 5 on vendor risk. Audit path scores 3 of 5: Sprinto names a partner network of audit firms and lets auditors review evidence inside the platform.
Best for
Best overall for ISMS scope, SoA and Annex A evidence automation
2. Vanta: Best for automatic Statement of Applicability generation, Vanta says
82/100
Strong (70 to 84)
Vanta features
Vanta ranks second at 82. Vanta says it automatically generates and updates the Statement of Applicability, mapping each ISO 27001 control to real tests and documents. Its risk management workflows are based on ISO 27005, and each risk in the register gets an inherent score, a treatment plan and a residual score. Vanta also says it supports ISO 27017, 27018 and 27701 as extensions to an ISO 27001 program, so a team can grow the certification scope without rebuilding the core ISMS. Vanta claims 400+ integrations and earns 5 of 5 on vendor risk through a TPRM Agent that monitors vendors continuously. Audit path scores 3 of 5: Vanta names audit partners and lets auditors review evidence inside the platform.
Best for
Best for automatic Statement of Applicability generation, Vanta says
The largest integration catalog in the SOC 2 ranking, with 5 of 5 on vendor risk. Pricing transparency is its weakest criterion, since no price appears on its site. Its audit path scores 3 of 5.
3. Drata: Best for linking ISMS risk assessments directly to controls and policies
76/100
Strong (70 to 84)
Drata features
Drata ranks third at 76. Drata says it links ISO 27001 risk assessments directly to controls and supporting evidence, so each risk drives the control owner and the evidence chain in one system. Policies connect to controls with tracked reviews, approvals and version history, and Drata keeps controls, ownership and evidence continuously updated for surveillance audits without a last-minute catch-up. Audit Hub is where auditors receive evidence requests, review documents and approve findings, and Drata names its Auditor Alliance as counting more than 175 audit firms. Audit path scores 3 of 5. Vendor risk scores 4 of 5 through its Third-Party Risk Management solution.
Best for
Best for linking ISMS risk assessments directly to controls and policies
Strong on custom automation, vendor risk and a named network of audit firms. Drata has no list price and describes its integrations only as "hundreds", which holds its score down.
4. Secureframe: Best for ISMS policy templates reviewed by former auditors
75/100
Strong (70 to 84)
Secureframe features
Secureframe ranks fourth at 75. Secureframe says its policy templates for ISO 27001 were developed and reviewed by former auditors, and that the platform lets a team design an ISMS aligned to both the ISO 27001 framework and its own objectives. Its risk management follows the ISO 27005 methodology, with NIST-based risk scenarios and dashboards showing heat maps and trend charts. Automated tests run continuously against connected systems, which keeps evidence fresh for surveillance audits. Audit path scores 2 of 5: Secureframe earns no credit for a named audit-firm network. Vendor risk scores 2 of 5, with advanced third-party risk on the higher Complete plan.
Best for
Best for ISMS policy templates reviewed by former auditors
The only vendor here with a real starting list price, and the deepest federal framework list. Vendor risk, audit path and pricing transparency are its weakest criteria, at 2 of 5 each.
5. Scrut: Best for a ready-to-use Annex A control set that supports both 2013 and 2022
72/100
Strong (70 to 84)
Scrut features
Scrut ranks fifth at 72. Scrut says it ships a ready-to-use control set aligned with Annex A, so a team can start working without building controls from scratch. The platform supports both ISO 27001:2013 and ISO 27001:2022, which matters for teams with existing certificates under the older version. Scrut offers a permission-based audit workspace where auditors view time-stamped evidence, mapped controls, signed policies and live control health, and a past audit cycle can be cloned for the next one. Vendor risk scores 5 of 5 through AI-scored vendor questionnaires and online source monitoring for breach data. Audit path scores 3 of 5.
Best for
Best for a ready-to-use Annex A control set that supports both 2013 and 2022
Score
72/100
Pricing
No list price.
Audit
Partner-network auditors, with an Audit Center for evidence review
6. OneTrust: Best for vendor risk and third-party supplier assessments as a separate package
64/100
Adequate (55 to 69)
OneTrust features
OneTrust ranks sixth at 64. Its Tech Risk and Compliance product covers IT risk management with Key Risk Indicator dashboards across assets, processes and vendors, plus a policy portal with approval workflows and sign-off tracking. These tools handle the documentation and risk tracking obligations inside an ISMS, though OneTrust's audit path scores 2 of 5, earning no credit for a named audit-firm network. Vendor risk scores 5 of 5: OneTrust sells Third-Party Risk Management as its own package, assessing vendors against more than 50 built-in control frameworks and monitoring third parties continuously.
Best for
Best for vendor risk and third-party supplier assessments as a separate package
Scores 5 of 5 on vendor risk management, through a Third-Party Risk Management package sold separately from Tech Risk & Compliance, and 5 of 5 on automated evidence. Trust and questionnaires earns no credit, pricing transparency scores 1 of 5 and audit path 2 of 5.
7. Thoropass: Best for ISO 27001 certification delivered by Thoropass Certification LLC, its accredited ISO 27001 subsidiary
52/100
Limited (35 to 54)
Thoropass features
Thoropass ranks seventh at 52 overall but scores 5 of 5 on audit path, the highest of the seven. Thoropass Certification LLC, its accredited ISO 27001 certification subsidiary, runs the audit inside the platform. A team that wants one contract covering the ISMS software and the certification audit gets exactly that here. Thoropass says its Risk Register gives a 360-degree view of risk on a configurable 4x4 or 5x5 dashboard, and links risk back to controls. Policy creation, review and acknowledgement run inside the platform. Vendor risk and customisation score 0 of 5, so a team that needs continuous vendor monitoring or custom Annex A controls beyond what ships out of the box will find limits here.
Best for
Best for ISO 27001 certification delivered by Thoropass Certification LLC, its accredited ISO 27001 subsidiary
Score
52/100
Pricing
No list price.
Audit
Delivered in-platform by Thoropass Assurance, a licensed CPA firm
The only vendor that delivers the audit itself, through its own licensed CPA firm. It scores 0 of 5 on vendor risk, customisation and pricing transparency, and 1 of 5 on automated evidence.
These scores reflect what vendors list, not how well a team executes a certification project. The SoA drafting workflow varies: Sprinto says it generates the SoA from the ISMS scope; Vanta says it maps each control to real tests. Neither claim changes a score, and neither is auditor-independent.
Thoropass ranks seventh overall but delivers the certification audit directly. A team comparing Thoropass to a higher-ranked platform should weigh the value of one contract versus a separate auditor relationship.
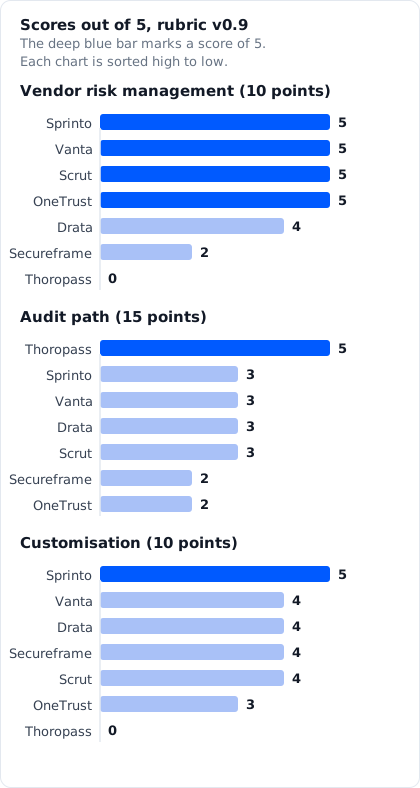
Scores out of 5 on three rubric criteria relevant to ISMS work. Source: rubric v0.9 scorecards.
On vendor risk (Annex A supplier controls), Sprinto, Vanta, Scrut and OneTrust score 5, Drata scores 4, Secureframe 2 and Thoropass 0. On audit path, Thoropass scores 5, Sprinto, Vanta, Drata and Scrut score 3, and OneTrust and Secureframe score 2. On customisation, Sprinto scores 5, Vanta, Drata, Secureframe and Scrut score 4, OneTrust 3 and Thoropass 0.
ISO 27001 add-ons are common. Sprinto sells Enterprise TPRM as an add-on, Drata sells custom frameworks as an add-on, and Vanta sells ISO 27017, 27018 and 27701 extensions separately.
Who should buy which
Teams building a first ISMS across ISO 27001 and another framework:Sprinto maps one Annex A control set across its digitized frameworks and drafts the SoA from the scope definition on day one.
Teams that want an automatically maintained SoA:Vanta says it generates and updates the SoA, mapping each control to real tests and documents as they change.
Teams that need risk assessments linked to controls:Drata connects each ISO 27001 risk assessment to its supporting controls and policy version history in one system.
Teams with legacy Annex A certificates under ISO 27001:2013:Scrut says it supports both the 2013 and 2022 versions on the same platform.
Teams running supplier assessments under Annex A 5.19 to 5.23:Sprinto, Vanta and Scrut each score 5 of 5 on vendor risk, and so does OneTrust. OneTrust sells its third-party package separately.
Teams that want the ISO 27001 audit delivered by the platform:Thoropass runs the ISO 27001 audit through Thoropass Certification LLC, its accredited ISO 27001 certification subsidiary, and ranks 7th overall.
Enterprise ISMS platforms outside the scored set
The vendors below describe their own scope. They are outside this site’s scored set, and the order is not a ranking.
DataGuard, Munich, covers ISO 27001:2022 and TISAX, and describes itself as a European security and compliance software platform used by more than 4,000 organizations in more than 50 countries.
Secfix, Berlin and Munich, says it automates ISO 27001, NIS2 and GDPR with more than 250 automated compliance checks, and targets EU companies.
HiScout, Berlin, says its GRC software has been used by German federal and state institutions for more than 15 years and covers BSI IT-Grundschutz alongside ISO standards.
ServiceNow sells Integrated Risk Management, which it describes as connecting risk and compliance across IT, cyber and business operations.
Archer describes one platform that unifies compliance, risk quantification and intelligence, with audit management and third-party governance in its product list.
MetricStream sells an AI-first GRC platform across risk, audit, compliance, cyber and resilience.
Best for ISO 27001 certification delivered by Thoropass Certification LLC, its accredited ISO 27001 subsidiary
52/100
No list price.
Delivered in-platform by Thoropass Assurance, a licensed CPA firm
4.7/5 (585 G2)
Conclusion
Sprinto takes first place for ISMS work at 84 out of 100, saying it drafts the SoA and automates Annex A evidence from day one. Vanta (82) says it generates the SoA automatically and adds ISO 27017, 27018 and 27701 extensions. Drata (76) links risk assessments to controls with full policy version history. Thoropass (52) scores lowest overall but delivers the ISO 27001 audit through Thoropass Certification LLC, its accredited ISO 27001 certification subsidiary.
Every score follows the public rubric, and its changelog records each change.
Sprinto ranks first at 84 out of 100 among the seven platforms scored here. Sprinto says it drafts the Statement of Applicability on day one and automates evidence for Annex A controls. Vanta is second at 82 and says it generates the SoA automatically. Drata is third at 76 and links risk assessments directly to ISMS controls.
What does ISMS software do?
ISMS software manages the components ISO 27001 requires: a risk register, a Statement of Applicability, Annex A control documentation, policy approvals, supplier assessments and an auditor's view of evidence. The platforms on this page automate evidence collection and keep controls current for surveillance audits between certification cycles.
Which ISMS platform handles the ISO 27001 audit directly?
Thoropass delivers the ISO 27001 audit through Thoropass Certification LLC, its accredited ISO 27001 certification subsidiary, and scores 5 of 5 on audit path. The other six connect a buyer to outside certification bodies or audit partners. Sprinto, Vanta, Drata and Scrut each name an audit-partner network and score 3 of 5 on audit path.
Which platforms automate the Statement of Applicability?
Sprinto says it drafts the SoA on day one. Vanta says it generates and updates the SoA automatically, mapping each control to real tests.
Which platforms support both ISO 27001:2013 and ISO 27001:2022?
Scrut says its platform supports both the 2013 and 2022 versions. The current edition of the standard is ISO/IEC 27001:2022. Organizations certified under the 2013 edition had until October 2025 to transition. An accredited certification body issues the certificate; ISO itself does not certify organizations.
Are there ISMS software options focused on the DACH market?
DataGuard, Secfix and HiScout are outside the scored set and serve the DACH market. DataGuard covers ISO 27001 and TISAX and describes itself as a European security and compliance platform. Secfix has offices in Berlin and Munich and automates ISO 27001. HiScout, Berlin, says its software has been used by German federal and state institutions for more than 15 years.