Seven GRC platforms scored on framework coverage, automated evidence, audit path, vendor risk and customisation. Sprinto leads at 84 out of 100, October 2026.
AT
The Audit Trail editorial desk
Updated Oct 11, 2026 · First published Oct 6, 2026
The best GRC platform among the seven scored here is Sprinto, at 84 out of 100. Vanta follows at 82, then Drata at 76, then Secureframe at 75, Scrut at 72, OneTrust at 64 and Thoropass at 52. All seven cover several security frameworks and are scored on the same rubric.
Sprinto, Vanta, Scrut and OneTrust score 5 of 5 on vendor risk, and OneTrust sells its third-party package separately. Drata says its Auditor Alliance counts 175+ audit firms, and Thoropass delivers the audit itself through its own CPA practice. Buyers shopping for larger GRC platforms also meet ServiceNow, Archer, Optro, MetricStream, LogicGate and Hyperproof, which sit outside the scored set.
Best for buying the platform and the audit as one engagement
52/100
Not published.
Delivered in-platform by Thoropass Assurance, a licensed CPA firm
4.7/5 (585 G2)
What GRC software covers
OCEG, the nonprofit that coined the term, defines GRC as “the integrated collection of capabilities that enable an organization to reliably achieve objectives, address uncertainty, and act with integrity.” Gartner defines GRC tools as supporting an “enterprise risk management (ERM) process” that runs from risk identification through assessment, mitigation, monitoring and reporting.
GRC software typically groups the work into a few parts. A risk register holds each risk with an owner and a treatment plan. A policy library records approvals and employee acceptance. Vendor risk reviews track suppliers, audit management gives auditors a view of evidence, and issue tracking ties each finding to a person. Reporting shows the state of every framework in scope.
Compliance management software covers the same parts for named security frameworks, and compliance automation is the layer of integrations and automated tests inside it. The seven platforms below are scored on the compliance management layer and the modules around it.
How we ranked these
All seven platforms rank on the same eight-criterion rubric as every other ranking here, including the SOC 2 compliance software ranking. The criteria run in priority order by weight: automated evidence (20 points), framework coverage and audit path (15 each), then pricing transparency, trust and questionnaires, vendor risk management, customisation and user sentiment (10 each).
Three criteria matter most to a GRC buyer: audit path, vendor risk management, and customisation, which asks whether a team can build a framework, control or test the vendor did not ship. A capability counts when the vendor lists it on any plan or add-on, and a roadmap item earns none.
1. Sprinto: Best overall for a multi-framework GRC program
84/100
Strong (70 to 84)
Sprinto product page, captured 24 September 2026
Sprinto ranks first at 84 out of 100. Its product list names Risk Management, Policy Management, Audit Management and Autonomous TPRM as separate modules, plus Unified Commitments for contracts and regulations. Policies get AI-assisted drafting and employee acknowledgement campaigns, and Growth-plan customers add multi-step approval workflows. Sprinto says Autonomous TPRM finds vendors as they show up, assigns a risk tier and keeps checking for changes, and its Enterprise TPRM add-on lists continuous monitoring and breach alerting, which earns vendor risk 5 of 5. Sprinto names 17 audit firms and allows a team to bring its own auditor on Growth. Bring-your-own frameworks and controls sit in the base feature list for every module, and the Growth plan card adds bring-your-own-controls.
2. Vanta: Best for a 400+ integration catalog, Vanta's claim
82/100
Strong (70 to 84)
Vanta homepage, captured 24 September 2026
Vanta ranks second at 82 and lists Continuous GRC as its own product line. Vanta says each risk in its register gets an owner, an inherent score, a treatment plan and a residual score, and that the register ships with 100+ common risk scenarios and suggested control mapping. Vanta also says issue tracking sits inside the GRC program, a Report Center produces stakeholder reports and business units can use separate Workspaces. Vendor risk scores 5 of 5 through a TPRM Agent that monitors vendors continuously, and Third Party Risk Management is sold standalone or as an add-on. Vanta claims a catalog of 400+ integrations.
Best for
Best for a 400+ integration catalog, Vanta's claim
The largest integration catalog in the SOC 2 ranking, with 5 of 5 on vendor risk. Pricing transparency is its weakest criterion, since no price appears on its site. Its audit path scores 3 of 5.
3. Drata: Best for Audit Hub evidence work and a 175+ firm Auditor Alliance, Drata says
76/100
Strong (70 to 84)
Drata homepage, captured 24 September 2026
Drata ranks third at 76. Drata says Enterprise GRC puts controls, risks, policies and evidence for several business units into one system, separate from its Compliance Automation product. Drata describes a risk register for internal risks, policy approvals with multiple approvers in ordered steps and event-driven workflows without code. Audit Hub holds evidence requests and approvals, and Drata says its Auditor Alliance counts 175+ audit firms. Vendor risk scores 4 of 5. Drata also sells Third-Party Risk Management as an independent solution, which Drata says is generally available. Custom frameworks are a paid add-on.
Best for
Best for Audit Hub evidence work and a 175+ firm Auditor Alliance, Drata says
Strong on custom automation, vendor risk and a named network of audit firms. Drata prints no price on its website and describes its integrations only as "hundreds", which holds its score down.
4. Secureframe: Best for a dedicated Defense plan alongside NIST-based risk scenarios
75/100
Strong (70 to 84)
Secureframe homepage, captured 24 September 2026
Secureframe ranks fourth at 75. Secureframe says its risk management follows ISO 27005 and that its dashboards show heat maps and trend charts. Policy templates are written and approved by former auditors, Secureframe says, and adding a framework generates policy addendums. Secureframe includes custom frameworks, controls and tests in its base plan. Vendor risk scores 2 of 5, and advanced third-party risk sits on the higher Complete plan. Fundamentals starts at $7,500 a year on secureframe.com, the only dollar price on a vendor's website among the seven.
Best for
Best for a dedicated Defense plan alongside NIST-based risk scenarios
5. Scrut: Best for GRC across regional frameworks such as MAS TRM, SAMA and RBI
72/100
Strong (70 to 84)
Scrut homepage, captured 24 September 2026
Scrut ranks fifth at 72. Scrut says its platform delivers Intelligent GRC. Scrut describes a custom risk register that links each risk to controls and routes treatment through workflows, and an Audit Center where auditors are invited with scoped access and a past audit can be cloned for the next cycle. Vendors come in through SSO or a CSV import, AI drafts the questionnaires, AI scores the responses and AI monitors online sources for vendor breach data, which earns 5 of 5 on vendor risk. Scrut says it supports 70+ frameworks, including MAS TRM, SAMA and RBI. Its 1,328 G2 reviews average 4.9, the top average of the seven.
Best for
Best for GRC across regional frameworks such as MAS TRM, SAMA and RBI
Score
72/100
Pricing
Not published.
Audit
Partner-network auditors, with an Audit Center for evidence review
6. OneTrust: Best for vendor risk bought as a separate package
64/100
Adequate (55 to 69)
OneTrust product page, captured 6 October 2026
OneTrust ranks sixth at 64 and earns 5 of 5 on vendor risk. OneTrust says its separately sold Third-Party Risk Management builds a vendor inventory, assesses vendors against 50+ built-in control frameworks, uses AI to ingest external risk evidence and monitors third parties continuously. Tech Risk & Compliance adds IT Risk Management, which OneTrust describes with Key Risk Indicator dashboards across assets, processes and vendors, plus a policy portal with approval workflows and sign-off tracking and issue and incident workflows from intake through remediation. OneTrust prints no dollar prices and prices its package by admin users and asset inventory. Trust and questionnaires earns no credit, which holds the total at 64.
Scores 5 of 5 on vendor risk management, through a Third-Party Risk Management package sold separately from Tech Risk & Compliance, and 5 of 5 on automated evidence. Trust and questionnaires earns no credit, pricing transparency scores 1 of 5 and audit path 2 of 5.
7. Thoropass: Best for buying the platform and the audit as one engagement
52/100
Limited (35 to 54)
Thoropass homepage, captured 24 September 2026
Thoropass ranks seventh at 52. It delivers the audit itself: Thoropass Assurance, its licensed CPA firm, runs audits inside the platform, and audit path scores 5 of 5, the highest of the seven. Thoropass says its Risk Register gives a 360-degree view of risk, offers 4x4 or 5x5 configurations and links risk back to controls. Thoropass also lists automated policy creation, review and acknowledgement. Vendor risk and customisation score 0 of 5, and thoropass.com prints no price. A buyer who wants the platform and the audit as one engagement gets that here.
Best for
Best for buying the platform and the audit as one engagement
Score
52/100
Pricing
Not published.
Audit
Delivered in-platform by Thoropass Assurance, a licensed CPA firm
The only vendor that delivers the audit itself, through its own licensed CPA firm. It scores 0 of 5 on vendor risk, customisation and pricing transparency, and 1 of 5 on automated evidence.
Rubric v0.9 has no criterion for risk registers or policy libraries, so register depth reaches the total only through the criteria around it. Vanta describes inherent and residual scoring, Thoropass says it offers 4x4 and 5x5 grids, Secureframe says it follows ISO 27005 and Scrut says each risk maps to controls. A score cannot show which of those fits a particular risk committee.
The totals also hide uneven modules. OneTrust ranks sixth overall but scores 5 of 5 on vendor risk and automated evidence, and Thoropass holds the top mark on audit path with 0 out of 5 on vendor risk and customisation.
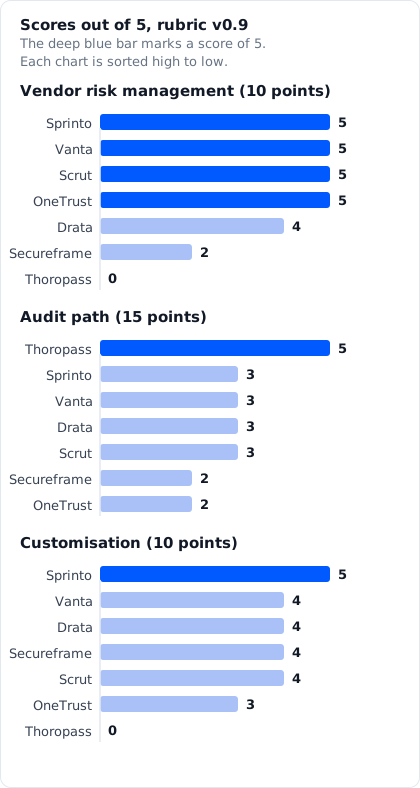
Scores out of 5 on three rubric criteria that GRC work leans on. Source: rubric v0.9 scorecards.
On vendor risk, Sprinto, Vanta, Scrut and OneTrust score 5, Drata scores 4, Secureframe 2 and Thoropass 0. On audit path, Thoropass scores 5, Sprinto, Vanta, Drata and Scrut score 3, and OneTrust and Secureframe score 2. On customisation, Sprinto scores 5, Vanta, Drata, Secureframe and Scrut score 4, OneTrust 3 and Thoropass 0.
Several GRC modules cost extra. Sprinto sells Enterprise Risk Management and Enterprise Vendor Risk Management as add-ons, Drata sells custom frameworks as an add-on, and Vanta sells Third Party Risk Management standalone or as an add-on. Secureframe puts advanced third-party risk on its Complete plan, and OneTrust sells Third-Party Risk Management as its own package.
Prices are scarce. Only Secureframe lists a dollar figure on its website, and the pricing study lists AWS Marketplace starting prices for six of the seven.
Who should buy which
Teams building a first GRC program across several frameworks:Sprinto lists risk, policy, audit and vendor modules together and offers one control set across frameworks.
Teams that want a risk register seeded with ready-made scenarios:Vanta says its register ships with 100+, and Secureframe says its risk library holds NIST scenarios.
Teams that run audits with outside firms:Drata keeps requests and approvals in Audit Hub, and it faces OneTrust in a head-to-head comparison.
Teams where vendor risk is the main job:OneTrust sells it as a separate package, and Sprinto, Vanta and Scrut score the same 5 of 5. Drata scores 4.
Teams with regional or defense obligations:Scrut says it supports MAS TRM, SAMA and RBI, and Secureframe sells a Defense plan that ranks in the CMMC compliance software list.
Teams that want the audit delivered by the platform vendor:Thoropass delivers the audit itself, which no other platform of the seven does.
Enterprise GRC suites outside the scored set
The vendors below describe their own scope. They are outside this site’s scored set, and the order is not a ranking.
ServiceNow sells Integrated Risk Management, which it describes as connecting risk and compliance across IT, cyber and business operations.
Archer describes one platform that unifies compliance, risk quantification and intelligence, with audit management and third-party governance in its product list.
Optro, formerly AuditBoard, markets a GRC system that covers risk-based audits, cyber risk, regulatory change and AI governance.
MetricStream sells an AI-first GRC platform across risk, audit, compliance, cyber and resilience.
LogicGate describes 30+ applications for enterprise risk, third-party risk, cyber risk and compliance management.
Hyperproof describes a platform that connects controls to risks and keeps a common control set across an enterprise.
Best for buying the platform and the audit as one engagement
52/100
Not published.
Delivered in-platform by Thoropass Assurance, a licensed CPA firm
4.7/5 (585 G2)
Conclusion
Sprinto takes first place for GRC work at 84 out of 100. Vanta (82) claims a 400+ integration catalog, Drata (76) pairs Audit Hub with a 175+ firm Auditor Alliance, Drata says, and OneTrust (64) sells vendor risk as a separate package.
Every score follows the public rubric, and its changelog records each change.
Sprinto ranks first at 84 out of 100 among the seven platforms scored here. Vanta is second at 82 and says its risk register ships with 100+ common scenarios, and Drata is third at 76. OneTrust ranks sixth overall and is one of four platforms scored 5 of 5 on vendor risk.
How is GRC software different from compliance management software?
GRC software covers governance, risk and compliance work for a whole organization, and Gartner defines GRC tools around an enterprise risk management process. Compliance management software handles one or more named frameworks such as SOC 2 and ISO 27001. The seven platforms on this page are scored on that framework layer and the modules around it.
Are these platforms the same as enterprise GRC suites?
No. ServiceNow, Archer, Optro (formerly AuditBoard), MetricStream, LogicGate and Hyperproof are outside this site's scored set, so no score or rank applies to them. Each describes its own scope. ServiceNow, for example, describes its Integrated Risk Management product as connecting risk and compliance across IT, cyber and business operations.
Which GRC platform has the strongest vendor risk tooling?
Sprinto, Vanta, Scrut and OneTrust score 5 of 5 on vendor risk management, and OneTrust earns it through a Third-Party Risk Management package it sells separately. Drata scores 4 of 5, Secureframe 2 and Thoropass 0.
Do GRC platforms publish their prices?
Rarely. Secureframe prints a Fundamentals starting price of $7,500 a year on secureframe.com. Sprinto, Vanta, Drata, Scrut, OneTrust and Thoropass print no dollar prices on their websites, and OneTrust prices its package by admin users and asset inventory.
Which of these platforms includes the audit?
Thoropass delivers the audit itself through Thoropass Assurance, its licensed CPA firm, and scores 5 of 5 on audit path. Sprinto, Vanta, Drata and Scrut score 3 of 5 and connect a buyer to outside firms. Drata says its Auditor Alliance counts 175+ audit firms.