Seven risk management platforms scored on risk registers, scoring methodology, treatment workflows and TPRM. Sprinto leads at 84 out of 100, November 2026.
Score 5 of 5 on automated evidence, worth 20 of 100 points
Full marks on frameworks
6 of 7
The five core frameworks plus three or more of ISO 42001, NIST, FedRAMP or CMMC
Audit sold with the platform
1 of 7
The audit comes in the platform deal or from an affiliated audit firm
The best risk management software among the seven scored here is Sprinto, at 84 out of 100. Vanta follows at 82, then Drata at 76, Secureframe at 75, Scrut at 72, OneTrust at 64 and Thoropass at 52. All are scored on the same rubric.
Sprinto, Vanta, Scrut and OneTrust score 5 of 5 on vendor risk management. OneTrust sells its third-party package separately. Vanta says its register ships with more than 100 prebuilt risk scenarios, and Drata links risk assessments to controls in one system. Thoropass scores lowest on vendor risk (0 of 5) but delivers an in-house audit through its own CPA practice. Buyers evaluating enterprise risk platforms also meet ServiceNow, Archer, LogicGate and Riskonnect, which sit outside the scored set.
Best for a risk register bundled with an in-house audit engagement
52/100
No list price.
Delivered in-platform by Thoropass Assurance, a licensed CPA firm
4.7/5 (585 G2)
What risk management software does
A risk register is the core: each risk gets a name, a likelihood, an impact, an owner and a treatment plan. The register feeds into the broader compliance program by linking each risk to the controls that address it, and by producing the residual risk picture an auditor or board needs to see.
Third-party risk management adds supplier assessments, questionnaires and continuous monitoring to the same register, covering the vendor-side exposure that internal tests alone do not reach. Treatment workflows route accepted risks, mitigated risks and transferred risks to the right owners with due dates and evidence requirements.
ISMS software covers the ISO 27001-specific layer of this work, including the Statement of Applicability and Annex A. GRC software covers governance and enterprise risk alongside compliance.
How we ranked these
All seven platforms rank on the same eight-criterion rubric as every other ranking on this site. The criteria run in priority order: automated evidence (20 points), framework coverage and audit path (15 each), then pricing transparency, trust and questionnaires, vendor risk management, customisation and user sentiment (10 each).
For a risk management buyer, two criteria carry extra weight here. Vendor risk management (10 points) measures whether the platform includes TPRM with continuous monitoring, questionnaire automation and AI-assisted vendor scoring. Customisation (10 points) asks whether a team can build a custom risk control or test beyond what ships out of the box. A capability counts when the vendor lists it on any plan or add-on.
1. Sprinto: Best overall for risk management with vendor discovery and continuous TPRM
84/100
Strong (70 to 84)
Sprinto features
Sprinto ranks first at 84 out of 100 on the risk management angle. Sprinto sells Risk Management as a named product, with a risk register, risk scoring and treatment workflows built into the module. Vendor risk scores 5 of 5: Sprinto says its Autonomous TPRM finds vendors as they appear in the stack, assigns a risk tier automatically and monitors them for changes. The Enterprise TPRM add-on extends that to continuous monitoring and breach alerting. Sprinto says its AI reviews vendor documents as part of periodic vendor assessments on the Foundation plan. The risk register also links back to controls in the same platform, so a risk treatment plan ties directly to the control evidence an auditor will review. No dollar list price appears on any plan.
Best for
Best overall for risk management with vendor discovery and continuous TPRM
2. Vanta: Best for a risk register with more than 100 prebuilt risk scenarios, Vanta says
82/100
Strong (70 to 84)
Vanta features
Vanta ranks second at 82. Vanta says its risk register ships with a prebuilt library of more than 100 common risk scenarios, each with suggested control mapping. Each risk gets an owner, an inherent score, a treatment plan and a residual score. Risk management workflows follow ISO 27005, which matters for ISO 27001 programs. Vanta also says each risk in the register links to issue tracking inside the GRC program, so a treatment task does not leave the risk management workflow. Vendor risk scores 5 of 5 through a TPRM Agent that monitors vendors continuously and runs AI-assisted security reviews of vendor documents. Vanta claims 400+ integrations, which feeds the risk signal from connected systems.
Best for
Best for a risk register with more than 100 prebuilt risk scenarios, Vanta says
The largest integration catalog in the SOC 2 ranking, with 5 of 5 on vendor risk. Pricing transparency is its weakest criterion, since no price appears on its site. Its audit path scores 3 of 5.
3. Drata: Best for linking risk assessments to controls and evidence in one system
76/100
Strong (70 to 84)
Drata features
Drata ranks third at 76. Drata says its Enterprise GRC connects ISO 27001 and other risk assessments directly to controls and supporting evidence, so the risk register and the control evidence live in the same system. Event-driven risk workflows run without writing code, and policies tie to controls with tracked reviews, approvals and version history. Vendor risk scores 4 of 5: Drata sells Third-Party Risk Management as an independent solution and says it pulls documents from a vendor's trust center to run assessments. Customisation scores 4 of 5, and no-code custom tests let a team add controls to the risk treatment plan.
Best for
Best for linking risk assessments to controls and evidence in one system
Strong on custom automation, vendor risk and a named network of audit firms. Drata has no list price and describes its integrations only as "hundreds", which holds its score down.
4. Secureframe: Best for ISO 27005-based risk scoring with heat maps and trend charts
75/100
Strong (70 to 84)
Secureframe features
Secureframe ranks fourth at 75. Secureframe says its risk management follows the ISO 27005 methodology and that its library covers NIST-based risk scenarios across fraud, legal, finance and IT. Dashboards present risk through heat maps, summary tables and trend charts, which suits a team presenting risk posture to a board. User Access Reviews and Vendor Access Reviews run as separate tools, so access risk is tracked independently of configuration risk. Vendor risk scores 2 of 5, with the advanced third-party risk module sitting on the higher Complete plan. Secureframe Fundamentals starts at $7,500 a year.
Best for
Best for ISO 27005-based risk scoring with heat maps and trend charts
The only vendor here with a real starting list price, and the deepest federal framework list. Vendor risk, audit path and pricing transparency are its weakest criteria, at 2 of 5 each.
5. Scrut: Best for a risk register that links each risk to controls with AI-scored vendor checks
72/100
Strong (70 to 84)
Scrut features
Scrut ranks fifth at 72. Scrut says its custom risk register maps each risk to controls and routes treatment through structured workflows. Vendor risk scores 5 of 5: Scrut says its AI drafts vendor questionnaires, scores the responses and monitors online sources for vendor breach data, which produces a continuous signal rather than a point-in-time review. Vendors come into the platform through SSO or a CSV import. Scrut also supports more than 70 frameworks out of the box, so a risk register covering multiple frameworks stays on the same platform. Scrut holds the highest G2 average of the seven, 4.9 from 1,328 reviews.
Best for
Best for a risk register that links each risk to controls with AI-scored vendor checks
Score
72/100
Pricing
No list price.
Audit
Partner-network auditors, with an Audit Center for evidence review
6. OneTrust: Best for third-party risk bought and managed as its own package
64/100
Adequate (55 to 69)
OneTrust features
OneTrust ranks sixth at 64 and earns 5 of 5 on vendor risk. OneTrust sells Third-Party Risk Management as its own package, separate from its Tech Risk and Compliance product. OneTrust says it builds a vendor inventory, assesses vendors against more than 50 built-in control frameworks, uses AI to ingest external risk evidence and monitors third parties continuously. Its IT Risk Management module within Tech Risk and Compliance adds Key Risk Indicator dashboards across assets, processes and vendors, with issue and incident workflows from intake through remediation. OneTrust prints no dollar prices and prices by admin users and asset inventory.
Best for
Best for third-party risk bought and managed as its own package
Scores 5 of 5 on vendor risk management, through a Third-Party Risk Management package sold separately from Tech Risk & Compliance, and 5 of 5 on automated evidence. Trust and questionnaires earns no credit, pricing transparency scores 1 of 5 and audit path 2 of 5.
7. Thoropass: Best for a risk register bundled with an in-house audit engagement
52/100
Limited (35 to 54)
Thoropass features
Thoropass ranks seventh at 52 and scores 0 of 5 on vendor risk. Thoropass says its Risk Register gives a 360-degree view of company risk, with tracking, evaluation and remediation on a configurable 4x4 or 5x5 dashboard, and links risk back to controls. Policy management and automated policy review run inside the same platform. What Thoropass does deliver is an in-house audit engagement: Thoropass Assurance, its licensed CPA firm, runs the audit inside the platform, which earns 5 of 5 on audit path. A team that needs risk register basics plus a bundled audit engagement can get both here, with vendor risk and custom framework work outside the scope.
Best for
Best for a risk register bundled with an in-house audit engagement
Score
52/100
Pricing
No list price.
Audit
Delivered in-platform by Thoropass Assurance, a licensed CPA firm
The only vendor that delivers the audit itself, through its own licensed CPA firm. It scores 0 of 5 on vendor risk, customisation and pricing transparency, and 1 of 5 on automated evidence.
Rubric v0.9 has no criterion for risk register depth or scenario quality. Vanta describes inherent and residual scoring from a prebuilt library, Thoropass says it offers 4x4 and 5x5 grids, and Secureframe says it follows ISO 27005. A score cannot capture how well a register fits a particular risk committee’s methodology.
Vendor risk scores separate sharply. Sprinto, Vanta, Scrut and OneTrust each score 5, and Thoropass scores 0. A team for whom TPRM is the core job should shortlist the top four on vendor risk and weigh their total scores alongside that criterion alone.
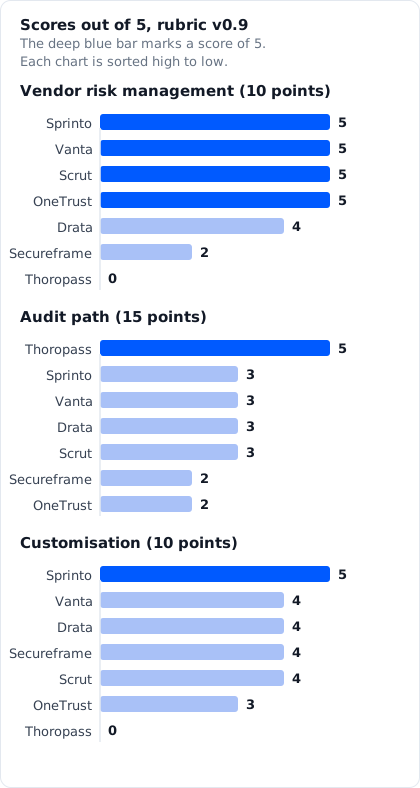
Scores out of 5 on vendor risk, audit path and customisation. Source: rubric v0.9 scorecards.
On vendor risk, Sprinto, Vanta, Scrut and OneTrust score 5, Drata scores 4, Secureframe 2 and Thoropass 0. On audit path, Thoropass scores 5, Sprinto, Vanta, Drata and Scrut score 3, and Secureframe and OneTrust score 2. On customisation, Sprinto scores 5, Vanta, Drata, Secureframe and Scrut score 4, OneTrust 3 and Thoropass 0.
Who should buy which
Teams that need automated vendor discovery alongside the risk register:Sprinto says Autonomous TPRM finds vendors as they appear and assigns a risk tier automatically. The Enterprise TPRM add-on adds continuous monitoring and breach alerting.
Teams that want a prebuilt risk scenario library:Vanta says its register ships with more than 100 common scenarios and suggested control mapping. Secureframe holds NIST-based scenarios across fraud, legal, finance and IT.
Teams connecting ISO 27001 risk assessments to controls:Drata links risk assessments directly to controls and policy version history in one system.
Teams presenting risk posture to a board:Secureframe uses heat maps, summary tables and trend charts, and its methodology follows ISO 27005.
Teams where vendor risk is the primary job:OneTrust sells Third-Party Risk Management as its own package, assessing vendors against 50+ frameworks and monitoring continuously. Vanta and Sprinto sell TPRM as a standalone or add-on.
Teams that need risk register and audit from one vendor:Thoropass combines a configurable risk register with an in-house audit engagement through its own CPA practice.
Enterprise risk management platforms outside the scored set
The vendors below describe their own scope. They are outside this site’s scored set, and the order is not a ranking.
ServiceNow Integrated Risk Management uses AI agents to continuously assess controls, monitor for emerging risks, identify gaps, and route remediation work to the right teams.
Archer Evolv Risk expresses exposure in financial terms rather than a color on a grid, so a risk in one business unit compares directly against a risk in another when funding is allocated.
LogicGate Risk Cloud connects risk to business objectives and delegates time-intensive intake and assessment workflows to fully-auditable agents.
Riskonnect positions its ERM platform as a flexible model that lets teams start anywhere, then add capabilities as the business grows.
SAP GRC organises enterprise risk and compliance, identity and access governance, cybersecurity, and international trade management as cohesive modules integrated with SAP S/4HANA.
Mitratech Alyne describes cloud-based, AI-driven GRC software for continuous risk monitoring that serves CISOs and risk professionals across assessment, compliance, analytics, and threat defense.
GBTEC Enterprise Risk offers portfolio simulation, scenario analysis, stress tests, and multi-year projections, and covers MaRisk requirements for BaFin-regulated organisations.
Best for a risk register bundled with an in-house audit engagement
52/100
No list price.
Delivered in-platform by Thoropass Assurance, a licensed CPA firm
4.7/5 (585 G2)
Conclusion
Sprinto takes first place for risk management at 84 out of 100, combining a named Risk Management product with Autonomous TPRM and 5 of 5 on vendor risk. Vanta (82) says its register ships with more than 100 prebuilt scenarios and matches Sprinto on vendor risk. OneTrust (64) sells Third-Party Risk Management as its own package and also scores 5 of 5 on vendor risk.
Every score follows the public rubric, and its changelog records each change.
What is the best risk management software for security compliance?
Sprinto ranks first at 84 out of 100 among the seven platforms scored here, with a named Risk Management product covering automated vendor discovery, AI review and continuous TPRM. Vanta is second at 82 with a prebuilt risk scenario library. Drata is third at 76 and connects risk assessments directly to controls in one system.
How is risk management software different from GRC software?
GRC software covers governance, risk and compliance together. Risk management software focuses on the risk register, risk scoring, treatment workflows and third-party risk monitoring inside a broader program. The platforms on this page each include a risk register as part of a GRC or compliance platform. The GRC software ranking covers all seven on the full set of GRC criteria.
Which platforms score highest on vendor risk management?
Sprinto, Vanta, Scrut and OneTrust each score 5 of 5 on vendor risk. Sprinto says it uses Autonomous TPRM with continuous monitoring, Vanta uses a TPRM Agent, and Scrut uses AI to score questionnaires and monitor sources. OneTrust sells Third-Party Risk Management as a separate package. Drata scores 4 of 5, Secureframe 2 and Thoropass 0.
Which risk registers come with prebuilt scenarios?
Vanta says its register ships with more than 100 common risk scenarios and suggested control mapping. Secureframe says its library holds NIST-based risk scenarios covering fraud, legal, finance and IT. Thoropass describes a 360-degree risk view on a 4x4 or 5x5 configurable dashboard. It earns no credit for a prebuilt scenario library.
Does risk management software replace a risk consultant?
The platforms on this page automate risk identification, scoring and treatment tracking for security frameworks. They do not replace a risk consultant for decisions about risk appetite, residual risk acceptance or regulatory interpretation. For ISO 27001, an external certification body reviews the risk treatment output during the certification audit.
Which platforms support third-party risk management as a standalone product?
OneTrust sells Third-Party Risk Management as its own package. Vanta sells Third Party Risk Management standalone or as an add-on. Sprinto sells Enterprise TPRM as an add-on to its core platform.